Cloud, IoT & Security
Cybersecurity Services That Protect Your Applications, Cloud and Data
Find and fix vulnerabilities before attackers do. We test, harden and monitor your web apps, mobile apps, APIs and cloud infrastructure, and help you meet the compliance standards your customers demand.
Overview
Security that keeps up with how fast you ship
Breaches are expensive, and enterprise buyers increasingly ask for security evidence before they sign. Our security engineers combine automated scanning with expert manual testing to uncover the issues that matter most.
Every engagement ends with a prioritised, developer-friendly report and, if you want, our engineers can fix the issues for you.
What we offer
Cybersecurity services
Web & API penetration testing
OWASP Top 10 and API Security Top 10 testing with proof-of-concept exploits and clear remediation steps.
Mobile app security testing
iOS and Android testing aligned with OWASP MASVS: storage, network, authentication and reverse engineering.
Cloud security assessment
AWS, Azure and GCP configuration reviews, IAM hardening and least-privilege access.
Secure code review & DevSecOps
SAST, DAST, dependency and secret scanning built into your CI/CD pipeline.
Compliance readiness
Gap analysis and controls for SOC 2, ISO 27001, GDPR, HIPAA and PCI DSS.
AI & LLM security
Prompt injection, data leakage and model abuse testing for AI-powered products.
Trusted by startups, scale-ups and global brands




How we work
A proven process from idea to impact
Discovery & consultation
We dig into your goals, users and constraints, then turn them into a clear scope, success metrics and a delivery roadmap.
Planning & architecture
We choose the right stack, design the system architecture and plan sprints so cost, timeline and risk are visible from day one.
Design & prototyping
Wireframes, UI design and clickable prototypes validated with real users before a line of production code is written.
Agile development
Two-week sprints with demos, AI-assisted engineering and code reviews. You see working software every sprint.
QA, security & launch
Manual and automated testing, security checks and performance tuning, then a smooth release to the cloud and app stores.
Growth & support
Monitoring, maintenance, analytics and continuous improvement so the product keeps getting better after launch.
Case studies
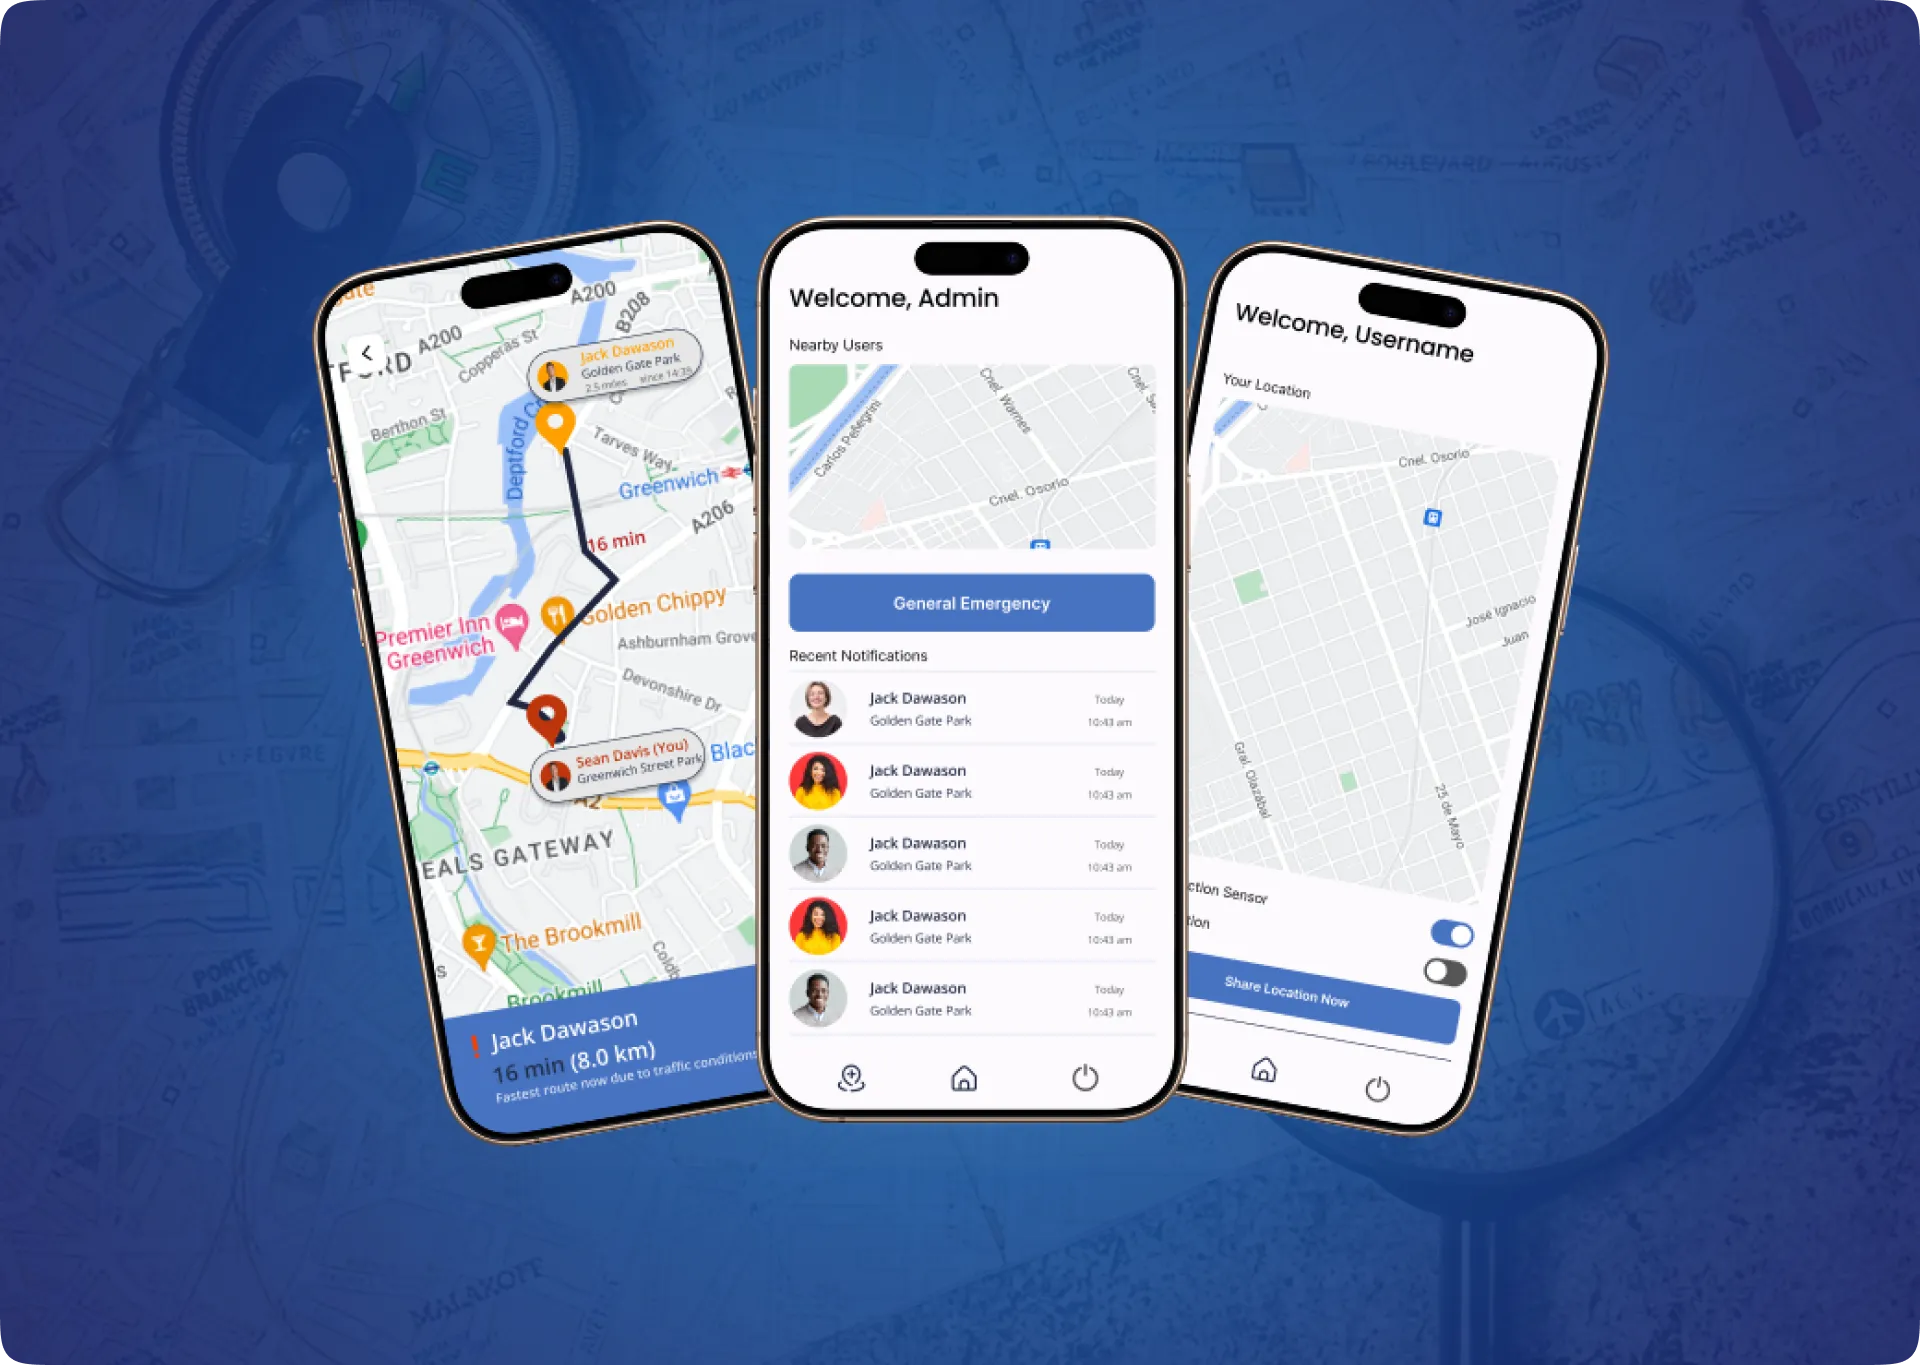
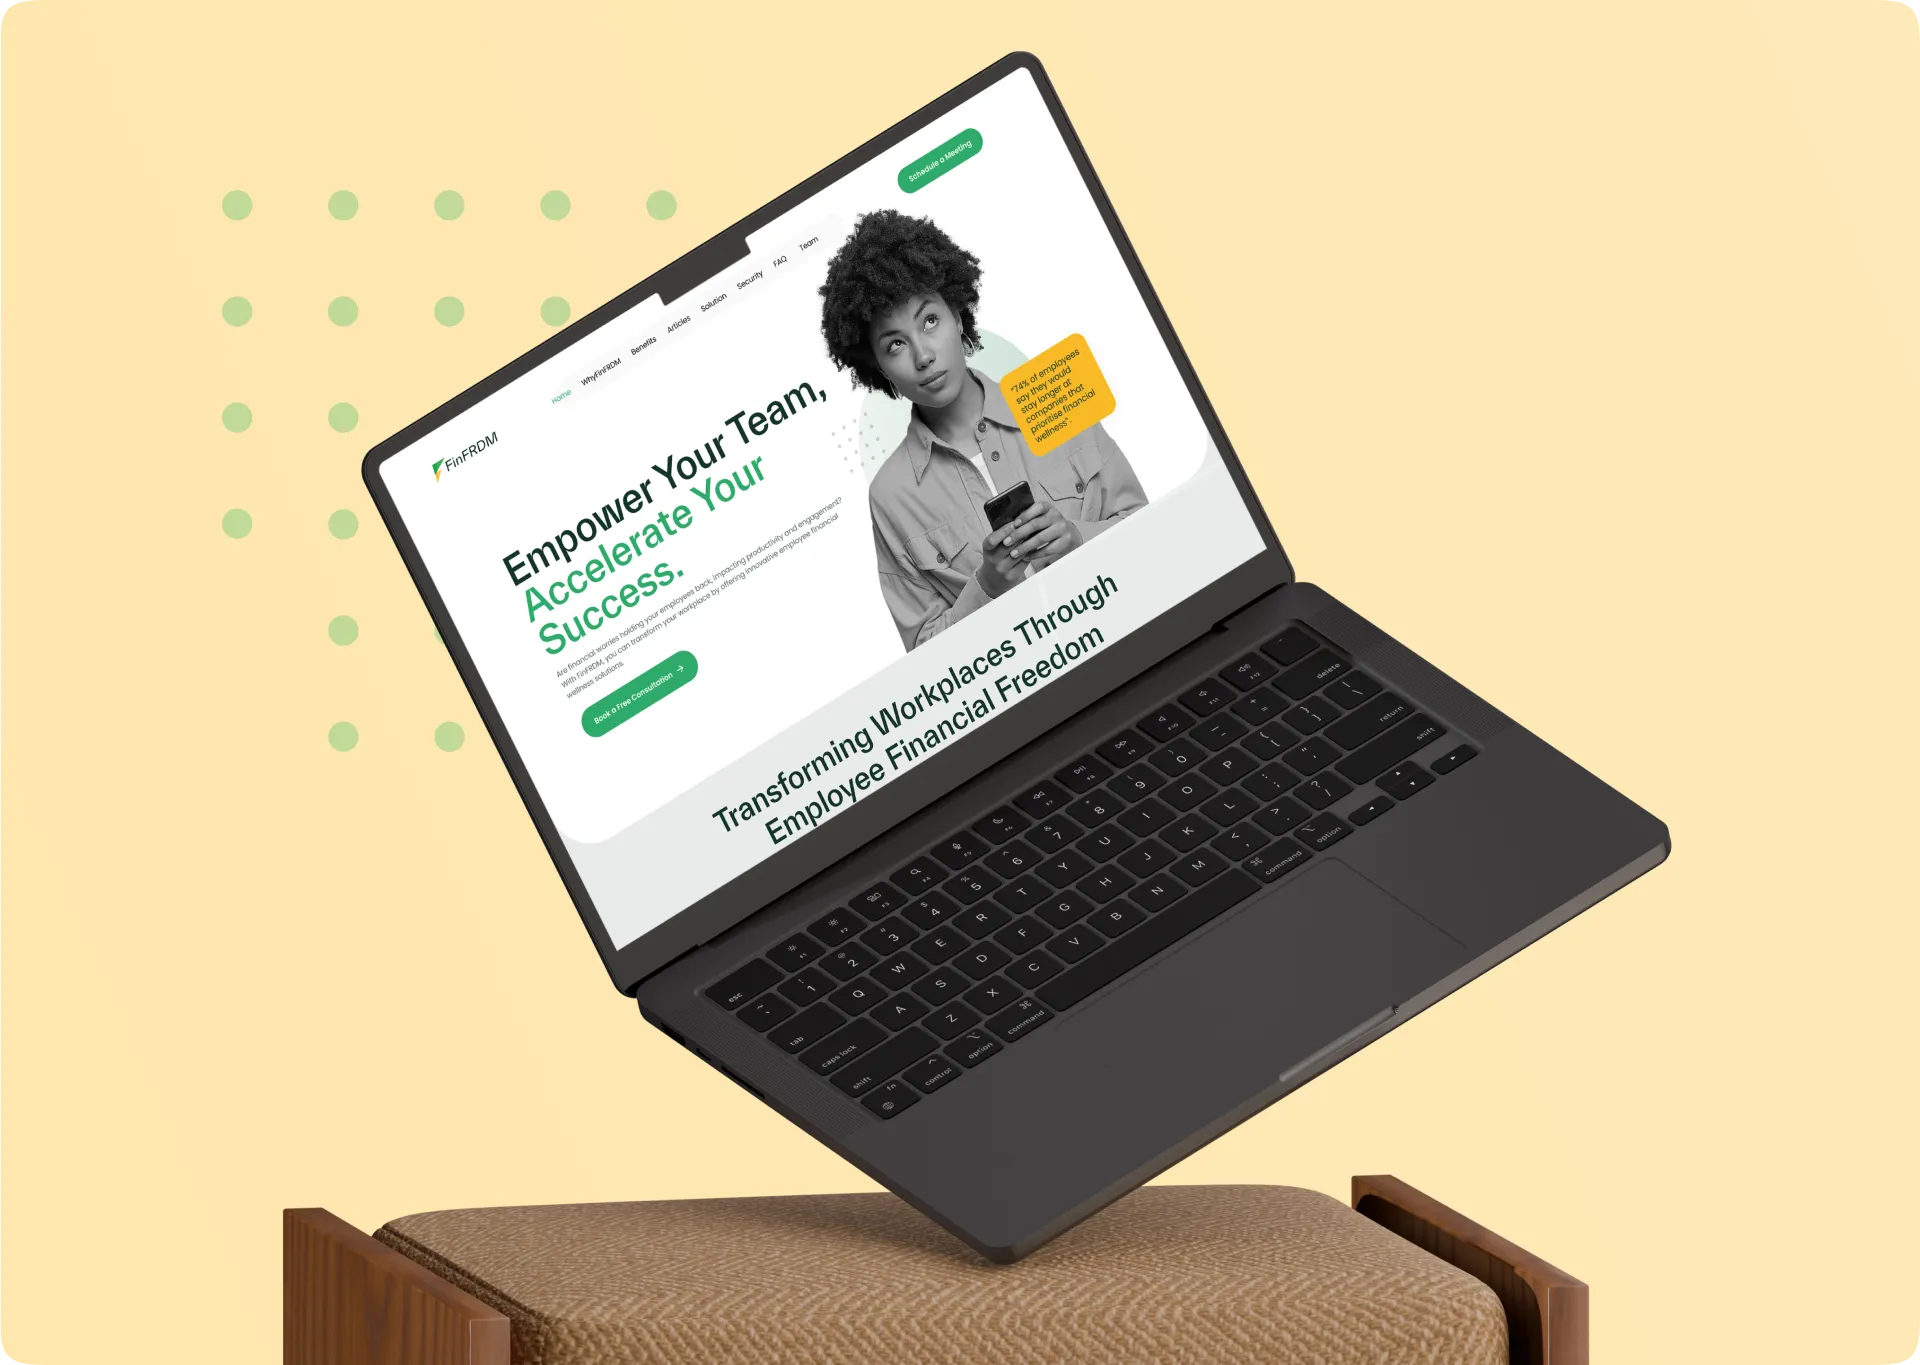
Our most successful projects
Why AIM Digital
Why companies choose AIM Digital Technologies
AI-first engineering
From idea to production, we take AI concepts to working proof of concept in as little as 90 days, and use AI tooling to ship everything faster.
Product-first mindset
We focus on outcomes, not outputs, aligning product strategy, engineering and UX with your business and customer goals.
Delivery excellence
Agile, high-velocity delivery with transparent sprints, demos and reporting. Reliable results without delays or excuses.
Industry insight
Deep experience across fintech, healthcare, real estate, e-commerce, logistics and education means practical solutions built for real impact.
Global delivery, local focus
Teams serving clients across the USA, Canada, UK, Europe, the Gulf, Singapore and Australia, with overlap across your working hours.
Security by design
Security is embedded, not added on. We build for compliance needs across healthcare, finance and enterprise systems.
Technologies we use
- OWASP
- Burp Suite
- Nessus
- AWS Security Hub
- Cloudflare
- Snyk
- SonarQube
- Wazuh
Pricing & timeline
How much does a security assessment cost in 2027?
Typical budgets and timelines with our senior team at $25–$40 per hour, including design, development, QA and project management.
| Scope | Timeline | Typical cost |
|---|---|---|
| Web application penetration testOWASP-based testing, report, fix guidance and re-test | 1–2 weeks | $1,000–$2,500 |
| Cloud security reviewConfiguration, access, logging and network review | 1–3 weeks | $1,000–$3,000 |
| Web, API and mobile pen testFull application surface with prioritised findings | 2–4 weeks | $2,000–$5,000 |
Every project is quoted individually after a free call. Get an instant estimate or ask for a fixed quote.
Ready to start your cybersecurity services project?
Get a free consultation and a clear plan in 30 minutes.
Engagement models
Choose the partnership model that fits your project
Flexible models that match your goals, timeline and budget. Switch as your needs change.
Project-based delivery
Fixed scope, fixed timeline. We own delivery end to end, from discovery to launch. Best for well-defined products and MVPs.
- Fixed price & milestones
- Dedicated project manager
- Weekly demos and reports
Dedicated product team
A cross-functional squad (PM, designers, engineers, QA) that works as an extension of your company on an evolving roadmap.
- Scale up or down monthly
- Full-time, focused team
- Your process, our talent
Staff augmentation
Add pre-vetted developers, AI engineers, QA or DevOps experts to your in-house team in days, not months.
- Start in 1–2 weeks
- Interview every candidate
- Replace anytime
Client reviews
Global client reviews that speak volumes
FAQ
Frequently asked questions
Can't find your answer? Ask our team.
How much does a penetration test cost?
A web application penetration test typically costs $1,000–$2,500, depending on the number of pages, roles and API endpoints. Testing a web app together with its API and mobile apps usually costs $2,000–$5,000, and a cloud security configuration review $1,000–$3,000. These figures use our rate of $25–$40 per hour, and the re-test after fixes is scoped upfront.
How long does a penetration test take?
Testing a typical web application takes one to two weeks, with the written report shortly after. Larger scopes covering APIs, mobile apps and cloud infrastructure take longer. After you fix the findings, a focused re-test confirms they are closed.
What do you get in a penetration test report?
An executive summary for leadership, a list of findings rated by severity, proof-of-concept evidence for each vulnerability, the business impact, and clear, developer-ready remediation steps. After the re-test you receive an updated report showing which issues are resolved, which is useful for customers' security reviews and audits.
How often should we run a penetration test?
At least once a year and after any major release, infrastructure change or acquisition. SaaS companies that sell to enterprises often test more frequently, and add automated scanning to CI/CD between tests. Many compliance frameworks and enterprise customers expect an annual test as a minimum.
What is the difference between a vulnerability scan and a penetration test?
A vulnerability scan is automated: tools check for known weaknesses and misconfigurations, quickly and cheaply. A penetration test is manual: security engineers think like attackers, chain weaknesses together and test business logic, such as accessing another customer's data, which scanners usually miss. You need scans continuously and a pentest periodically.
Black box, grey box or white box testing: which do we need?
Grey box is the best value for most companies: testers get user accounts and some documentation, so they spend time finding real vulnerabilities rather than guessing. Black box simulates an outside attacker with no information. White box adds source code review and finds the most issues, at higher cost.
Will security testing disrupt our production systems?
No. We agree scope, timing and rules of engagement in writing before starting, and prefer to test against a staging environment that mirrors production. Any production testing is carefully controlled, avoids destructive actions and is coordinated with your team.
Can you fix the vulnerabilities you find?
Yes. Unlike testing-only firms, we have engineering teams who can remediate findings in your code and cloud setup, then re-test to confirm each fix. Or your own developers can fix them using our step-by-step guidance; either way we verify the result.
Can you help us get ready for SOC 2 or ISO 27001?
Yes. We run a gap analysis against the framework, then help implement the missing technical controls such as access management, logging, encryption, backups, vulnerability management and secure change processes, and organise evidence. Certification or the SOC 2 report itself comes from an independent auditor; we get you ready for it.
Do you assess HIPAA, GDPR and PCI DSS security requirements?
Yes. We review your applications and infrastructure against the technical safeguards in HIPAA, GDPR and PCI DSS, such as encryption, access control, audit logging, data retention and network segmentation, and give you a prioritised plan to close the gaps. Legal interpretation remains with your compliance or legal advisers.
Can you test AI and LLM applications for prompt injection?
Yes. We test AI chatbots and agents for prompt injection, data leakage between users, jailbreaks, unsafe tool use and excessive permissions, following the OWASP Top 10 for LLM applications. We then help add guardrails, output filtering and approval steps for risky actions.
What do you need from us to start a security assessment?
A signed NDA and scope agreement, the URLs, apps, APIs or cloud accounts to test, test user accounts for each role, the testing window, and a technical contact. For grey or white box testing, API documentation or source code access helps us find more in less time.
Related services
DevOps & Cloud
CI/CD, infrastructure as code, Kubernetes and cloud cost optimisation.
Learn moreSoftware QA & Testing
Functional, performance, security and mobile testing for flawless releases.
Learn moreAI Agents & Automation
Autonomous AI agents, copilots and workflow automation that handle real work across your tools.
Learn moreExplore more about cybersecurity services
Industries we build for
Hire & pricing
Guides & services
Global delivery
Cybersecurity Services for clients worldwide
Delivered from our Islamabad head office for companies across North America, Europe, the Gulf and Asia-Pacific.
North America
Middle East
South Asia
Free consultation
Let's talk about your cybersecurity services project
Tell us about your project and get a free 30-minute consultation with a senior engineer. You'll leave with clear next steps, whether you work with us or not.
- Reply within one business day
- NDA on request, 100% IP ownership
- Clear scope, timeline and estimate
- Talk directly to senior engineers